Skip to content
OmniGuest

Security & privacy

Isolation, private AI and an append-only audit log — as architecture, not as a checkbox.

Hotels hand us guest names, stays, preferences and conversations. OmniGuest is designed to meet GDPR, SOC 2 and PCI-DSS SAQ-A-EP requirements; the controls below describe how the platform is built today, not what a certificate promises.

Passkeys first. Passwords as the exception.

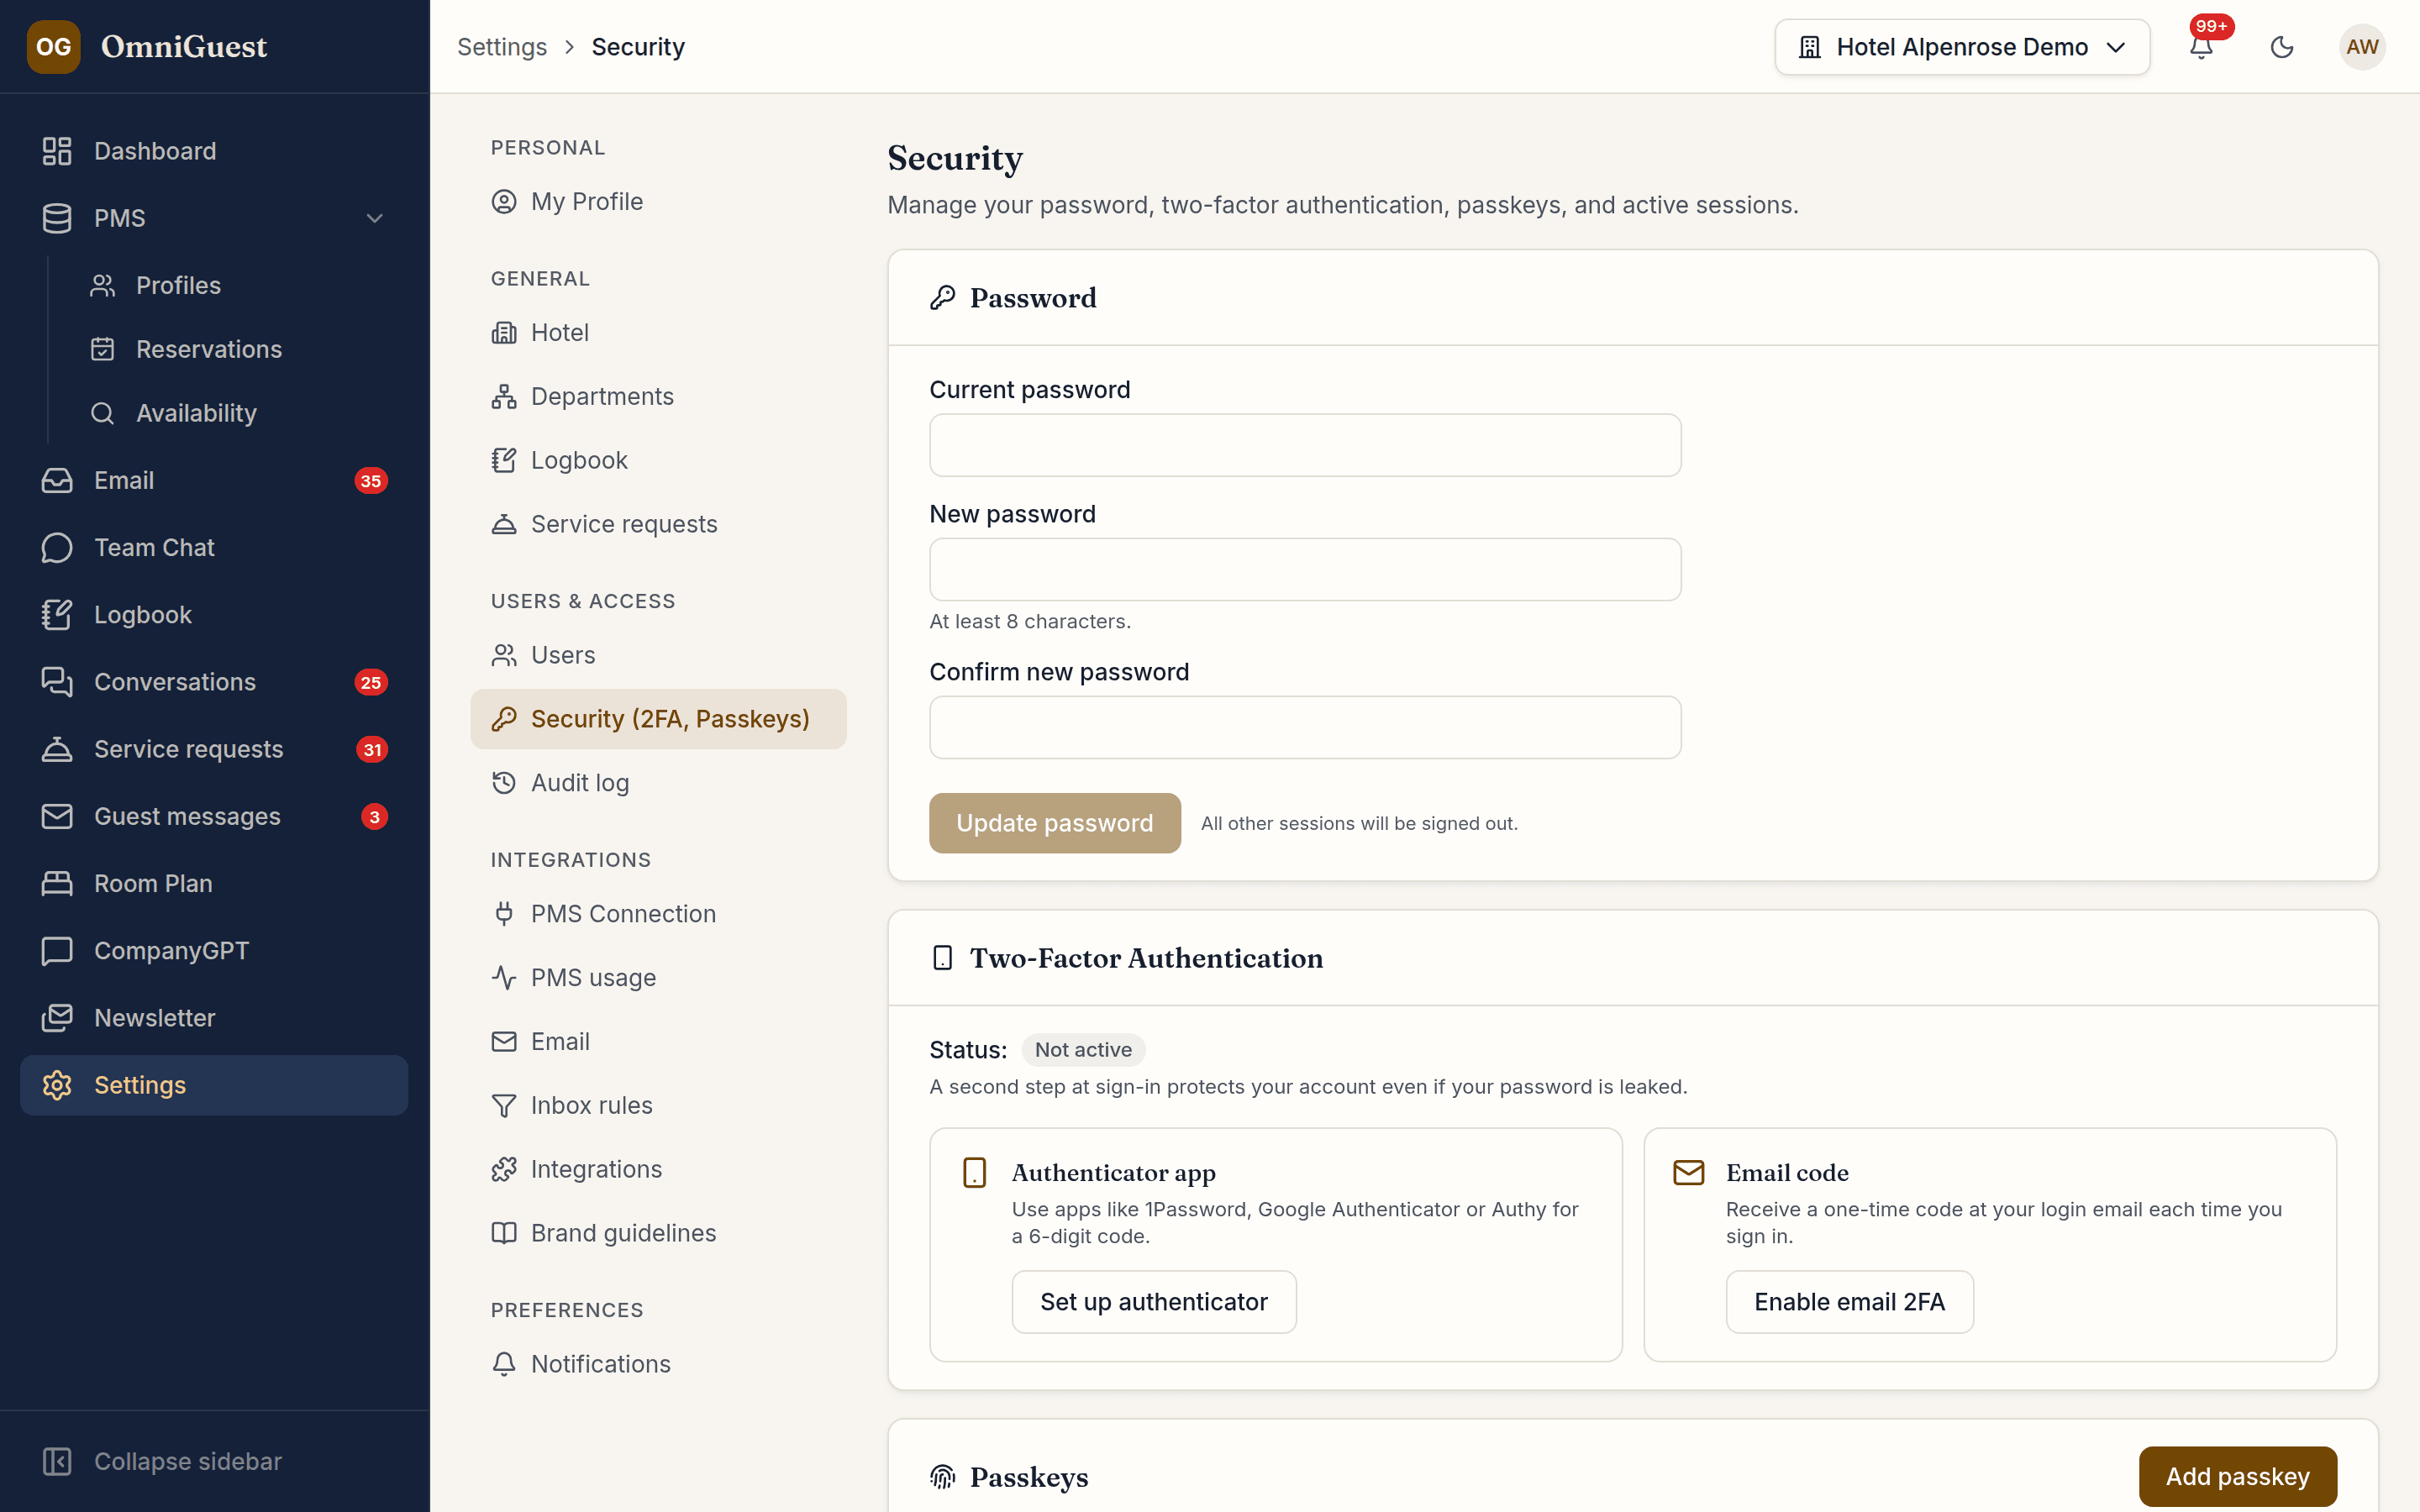
Every staff member signs in with a phishing-resistant passkey; two-factor codes and session control are one screen away. Administrators see who is signed in where and can end sessions remotely.

OmniGuest security settings with password, two-factor authentication and passkeys
  • Tenant isolation: one schema per enterprise

    Each hotel group runs in its own PostgreSQL schema on application nodes we operate. Guest records never share a table with another group.

    • Schema-per-enterprise with per-hotel scoping inside
    • Every request is scoped to its tenant's schema
    • Dedicated database instances can be arranged for enterprise customers
  • Private AI infrastructure

    Language, vision and speech models run on OmniGuest GPUs. By default prompts, documents and guest data never reach a public AI API; web search queries go to public search engines, and an external model fallback stays off unless a hotel switches it on.

    • Open-weight models served in-house behind a private gateway
    • No training on customer data — ever
    • Separate retrieval index per enterprise
  • Phishing-resistant authentication

    Passkeys (WebAuthn) are the primary login. Passwords with a second factor — authenticator app or e-mail code — remain available for transition.

    • Signed, revocable tokens issued by a central identity service
    • Custom roles and permissions per enterprise and hotel
    • Session overview with sign-out of other devices
  • Audit log

    Changes made by staff — PMS writebacks, bookings, notes, rules, permissions and settings — are recorded with actor, time and before and after values. Every guest message keeps its own delivery history.

    • Append-only: entries cannot be edited or deleted
    • History tab per reservation and profile, CSV export
    • Pseudonymisation of a person's entries for GDPR requests
  • Uploads are virus-scanned

    E-mail attachments, documents, photos, imports and design assets are scanned before they are stored. If a file cannot be scanned, it is refused rather than let through.

    • Fail-closed scanning on every upload path
    • Infected files are never delivered to staff or guests
    • Ticket photos from phones are converted and stripped of location data
  • Encrypted credentials

    PMS and mailbox credentials are encrypted at rest.

    • Integration secrets stored encrypted, never in plain text
    • OAuth wherever the provider supports it
  • Hosting in Europe

    Application, database and AI inference run on OmniGuest servers in the EU.

    • Application, database and inference in the EU
    • HTTPS for every connection to the platform
  • Deletion on request

    Guest data stays in its enterprise schema. At the end of a contract, or on request, we delete an enterprise's data; for an individual GDPR request, that person's audit-log entries are pseudonymised.

    • One schema per enterprise, so its data can be removed as a whole
    • Audit-log pseudonymisation without breaking the log
  • PMS writeback you switch on

    Nothing is written into your PMS until a hotel switches writeback on. Each kind of change can be switched off on its own and is limited to the roles allowed to make it.

    • Queue-based writeback with retries and an outbound list
    • Every write is read back from OPERA Cloud to confirm it
    • PMS always wins on conflicts
  • Compliance posture

    Designed to meet GDPR, SOC 2 and PCI-DSS SAQ-A-EP requirements. We provide a data processing agreement, sub-processor list and architecture documentation for your security review.

    • DPA and sub-processor list on request
    • Security questionnaire support for enterprise buyers
    • Payment card data is never stored by OmniGuest (planned payments module uses tokenisation)

A note on certifications

OmniGuest is designed to meet GDPR, SOC 2 and PCI-DSS SAQ-A-EP requirements. We do not claim certifications we do not hold. For your vendor assessment we provide architecture documentation, a data processing agreement, the sub-processor list and answers to your security questionnaire — ask for them in the demo.

Bring your security questionnaire.

We answer it in the first call, with the architecture on screen. Isolation, AI hosting, retention — every question has a concrete answer.